Source Code Capital Portfolio | "Xuanjing Security" Announces Completion of Hundreds of Millions of RMB Series B Financing Led by Source Code Capital

Deep coverage of the enterprise security market
#MaKe Key Updates from Source Code Capital and MaHui Members
On March 22, 2022, Xmirror Security, a leading DevSecOps agile security vendor, officially announced the completion of its Series B financing of several hundred million RMB. This round was led by Source Code Capital, with follow-on investment from GGV Capital and continued support from HSG. Xmirror Security will further deepen its strategic investment in key technology innovation for China's software supply chain security and forward-looking layout of the upstream and downstream industrial ecosystem. Leveraging its leading next-generation agile security framework, the company will build a closed-loop third-generation Xmirror DevSecOps intelligent adaptive threat management system for emerging application scenarios including DevSecOps agile security, software supply chain security, and cloud-native security, while continuously upgrading its large-scale product service delivery and operational capabilities across North China, East China, South China, Central China, Southwest China, and Hong Kong and Macao, with deep coverage of enterprise-level security markets including financial services, e-commerce, energy and power, intelligent manufacturing, telecom operators, and the broader internet sector.
Ziya, Founder and CEO of Xmirror Security, stated that the essence of security is the dynamic balance between risk and trust. Over the years, Xmirror has been focused on one thing: helping enterprise users better embrace change and more rapidly adapt to the proliferation of cloud-native technologies, to achieve endogenous agile security. Compared with traditional native software applications, we can see a clear technological trend: the vast majority of digital applications released in the future will be secure and trustworthy, empowered by code vaccine technology to enable self-detection of inherent flaws and risks within applications, as well as factory-default immunity against external unknown threats.
Xmirror Security specializes in integrated detection and defense against continuous threats in the DevSecOps software supply chain. Its original Xmirror DevSecOps intelligent adaptive threat management system primarily covers key stages from threat modeling, open source governance, risk discovery, and threat simulation to detection and response, offering development-operations-integrated agile security products and software supply chain security services featuring practical offensive and defensive confrontation, helping enterprise organizations gradually build an endogenous active defense system that adapts to their own business elasticity, enables agile business delivery, and leads future architecture evolution.
Currently, enterprises and institutions practicing Xmirror's agile security philosophy and applying its solutions include the People's Bank of China, China UnionPay, Bank of China, Industrial and Commercial Bank of China Limited, SPD Bank, Bank of Chongqing, Guangzhou Rural Commercial Bank, Suzhou Rural Commercial Bank, China Zheshang Bank, SHEIN, Ping An Insurance (Group) Company of China, Ltd., China Securities Co., Ltd., Shanghai Stock Exchange, Sinopec, PetroChina, China Telecom Group Co., Ltd. Research Institute, China Mobile Research Institute, China Unicom Research Institute, China Sports Lottery, People's Daily Online, State Grid Corporation of China, Peking University, ZTE, China Academy of Engineering Physics, Xpeng Motors, Dongfeng Nissan, Changan Automobile, China Automotive Engineering Research Institute, China Southern Airlines, and numerous other industry benchmark users.
Yungang Huang, Partner at Source Code Capital, the lead investor in this round, said: "DevSecOps is the inevitable trend toward security agility in the context of cloud-native computing. Centered on threat management and integrating multiple toolchains, the DevSecOps system enables enterprises to embed security throughout the entire software lifecycle from development to operations, and will inevitably become a critical component of enterprise digital infrastructure. We are very optimistic about Xmirror Security's technological foresight in the DevSecOps domain, and Xmirror's products have already gained recognition from multiple important clients across industries. We look forward to Xmirror creating tremendous value for customers in a future where IT infrastructure is accelerating cloud migration and the security environment is becoming increasingly complex."
Agile Security Governance from the Source of Development
According to authoritative third-party surveys, nearly 92% of known security vulnerabilities occur in software applications, and every 1,000 lines of application code contains at least one business logic flaw. Additionally, 78%-90% of modern applications incorporate open source components, with an average of 147 open source components per application, and 67% of applications use open source components with known vulnerabilities. Currently, for the vast majority of enterprise users, discovery of business application vulnerabilities comes from internal self-testing at best, and mostly from external third-party security researchers or vendors. The cost of fixing security vulnerabilities at different stages of the software development lifecycle varies dramatically — the cost difference between the R&D testing phase and the online operations phase can reach hundreds of times. Therefore, front-loading security work, eliminating vulnerability risks and open source threats at their inception, preventing applications from going live with vulnerabilities, and ensuring software supply chain security are extremely urgent and necessary.
One of Xmirror Security's flagship products, Lingmai IAST (Interactive Application Security Testing), serves as the application risk discovery platform in the pre-launch testing phase of the Xmirror DevSecOps intelligent adaptive threat management system. Through next-generation full-scenario real-time data flow contextual analysis technologies — including runtime application instrumentation (with dynamic taint tracking and interactive defect localization), terminal traffic proxy, bypass traffic mirroring, host traffic sniffing, heuristic crawling, and real-time Web log analysis — combined with original AI-heuristic penetration testing technology, it empowers traditional IT practitioners to rapidly establish an internal security crowdsourced testing model within client organizations. This enables traditional security novices (such as developers, testers, and QA personnel) to transparently achieve deep business security testing while completing application functional testing, with runtime dynamic monitoring of open source risks and precise coverage of over 95% of medium- and high-risk vulnerabilities, effectively preventing applications from going live with vulnerabilities.
Xmirror Lingmai IAST Gray-Box Security Testing Platform
Measuring Security Effectiveness Through Intelligent Offense and Defense
As Sun Tzu's The Art of War states: "The art of war teaches us to rely not on the likelihood of the enemy not coming, but on our own readiness to receive him; not on the chance of his not attacking, but rather on the fact that we have made our position unassailable." Offensive and defensive confrontation is an eternal theme in cybersecurity construction, and the most direct way to test the effectiveness of existing security systems in defending against unknown threats, such as continuous security crowdsourced testing, irregular offensive and defensive drills, and supporting detection and response measures.
Another flagship product from Xmirror Security, Lingmai BAS (Breach and Attack Simulation), serves as the automated threat simulation and security validation platform in the operations phase of the Xmirror DevSecOps intelligent adaptive threat management system. It is the first in China to implement an intelligent offensive and defensive drill robot system combining "AI + threat simulation," creatively transforming the practical experience accumulated by security experts through extensive penetration testing into structured experience that machines can store, recognize, and process. During automated testing, it leverages artificial intelligence algorithms for continuous "self-thinking" and logical reasoning decision-making, conducting complete invasion simulation and security measurement processes against given targets in a manner close to actual expert penetration testing — from information gathering, scanning and probing, vulnerability discovery, vulnerability exploitation, post-exploitation, to continuous validation. This comprehensively tests the effectiveness of existing security defense measures for client users, continuously and dynamically assesses the target organization's security posture from a "real hacker" perspective, and significantly addresses the problems of uneven security personnel capabilities and low efficiency.
Empowering Factory-Default Immunity with Code Vaccine Technology
With the rapid development of cloud-native technology, the swift proliferation of open source applications, and the large-scale implementation of DevSecOps practices, cybersecurity is evolving from perimeter security to endpoint security and then to application security. The technological focus of next-generation application security will be runtime contextual awareness.
One of the key products in Xmirror Security's "active defense" system, Yunsha RASP (Runtime Application Self-Protection) adaptive threat immunity platform, serves as the detection and response platform in the operations phase of the Xmirror DevSecOps intelligent adaptive threat management system. Through patented application vulnerability attack immunity algorithms, runtime security切面 scheduling algorithms, deep AI detection engines for Webshell, and deep traffic learning algorithms, it achieves deep integration of RASP and IAST key technologies, "injecting" active defense capabilities into digital business applications. With powerful application contextual analysis capabilities, it can capture and defend against various attack methods that bypass traffic detection (such as segmented transmission, encoding obfuscation and变形, application memory马, etc.), providing endogenous active security immunity capabilities with both business透视 and functional decoupling, ushering in innovative development for factory-default security immunity of business applications.
Latest Research and Practical Achievements in Xmirror DevSecOps
Drawing on years of practical experience in agile security implementation and software supply chain security research, Xmirror Security has developed a third-generation DevSecOps intelligent adaptive threat management system based on original patented "agile process platform + key technology toolchain + componentized software supply chain security services."
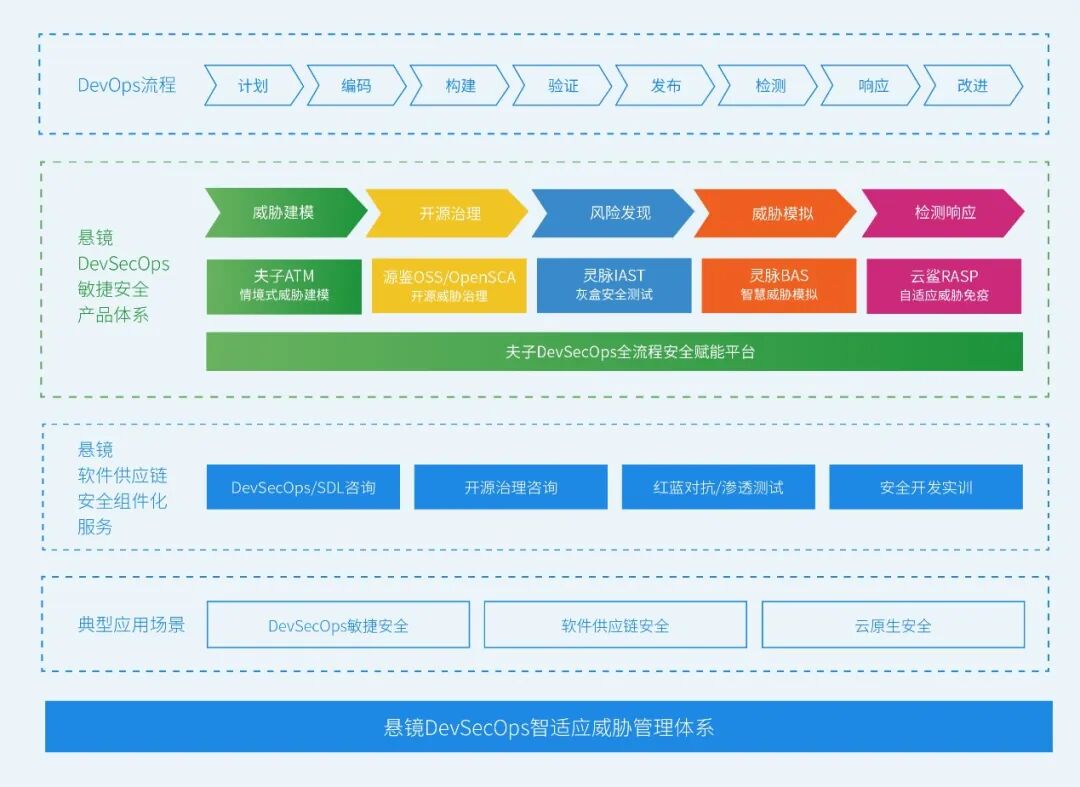
Xmirror Third-Generation DevSecOps Intelligent Adaptive Threat Management System
As a full-process agile security empowerment platform for DevSecOps, it emphasizes gentle, low-intrusiveness technology implementation from its very conception. Starting from several key practice points that drive the continuous operation of the DevSecOps CI/CD pipeline, it empowers existing personnel in enterprise organizations through technological innovation in threat modeling, open source governance, risk discovery, threat simulation, and detection and response, helping users gradually build an endogenous active defense system that adapts to their own business elasticity, enables agile business delivery, and leads future architecture evolution.
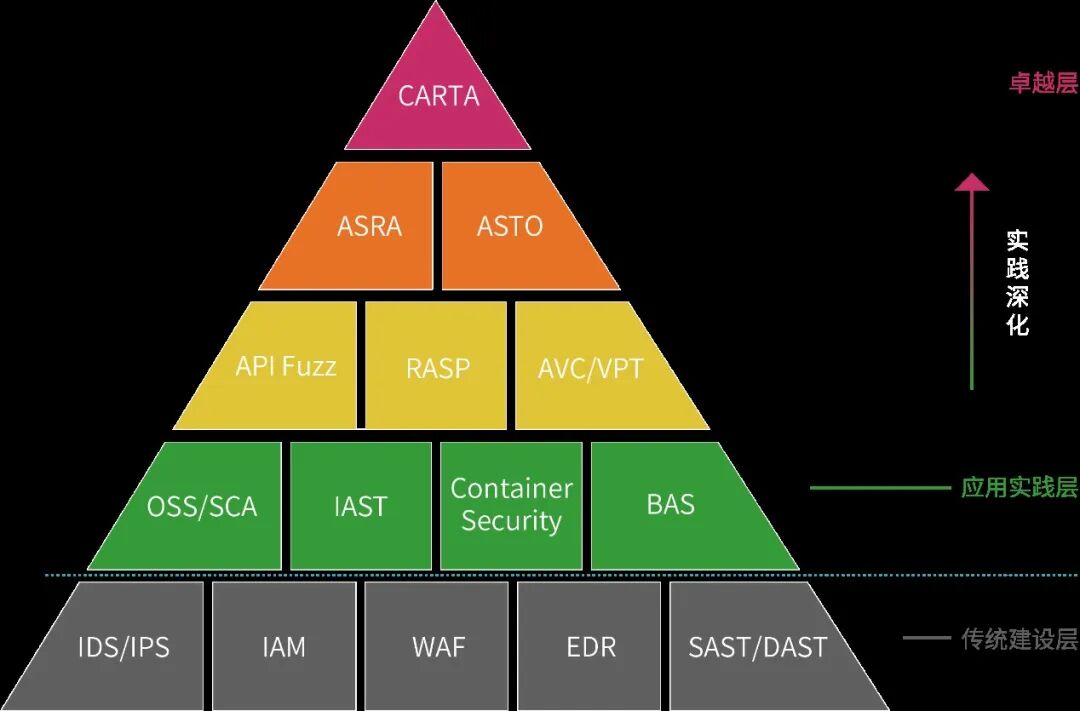
DevSecOps Agile Security Tools Pyramid v2.0
The DevSecOps Agile Security Tools Pyramid, as an annual in-depth research and practice output from Xmirror Security, provides forward-looking predictions for the evolution path of future DevSecOps key technologies, pointing the direction for subsequent systematic security construction by organizations in the industry.
MaKe|Nutshell Therapeutics Announces $40 Million Series A+ Financing, with Existing Shareholder Source Code Capital Continuing to Increase Stake
MaKe|Fairino Announces Over $50 Million Series B Financing, Led by Source Code Capital
 MaKe|New Retail Home Technology Brand "Banrixian"
Announces Completion of Tens of Millions of RMB in Pre-Series A Financing
Led by Source Code Capital

MaKe|Digital Consumer Goods Group "Dongfang Honghu"
Announces Completion of Tens of Millions of USD in Series A Financing
Exclusive Investment by Source Code Capital

MaKe|Metaverse Social Platform "BUD"
Announces Completion of $15 Million Series A+ Financing
Source Code Capital Participates in Investment
For more Source Code Capital portfolio companies, click "Read Original" to view